Servicing Rollout and Architecture Upgrades
Microsoft has formally declared the general availability of Windows 11 version 26H2, commencing a phased worldwide rollout for compatible desktop and notebook hardware. Rather than altering user interface conventions, this annual release targets underlying platform responsiveness, scheduling refinement, and reduced update overhead. Systems operating on current builds will progressively encounter the upgrade notification through the standard operating system update channel, managed via cloud cadence algorithms designed to evaluate hardware telemetry before initiating the payload transfer.
Architecture teams implemented this iteration primarily through an enablement package structure for machines already maintaining recent servicing stacks. Consequently, standard update installation requires only a concise restart cycle without extensive downtime or multi-stage offline phases. Corporate environments utilizing centralized management frameworks can immediately stage the release packages across test rings to validate enterprise software stacks and security tooling.
Core Kernel Optimization and Decoupled Modules
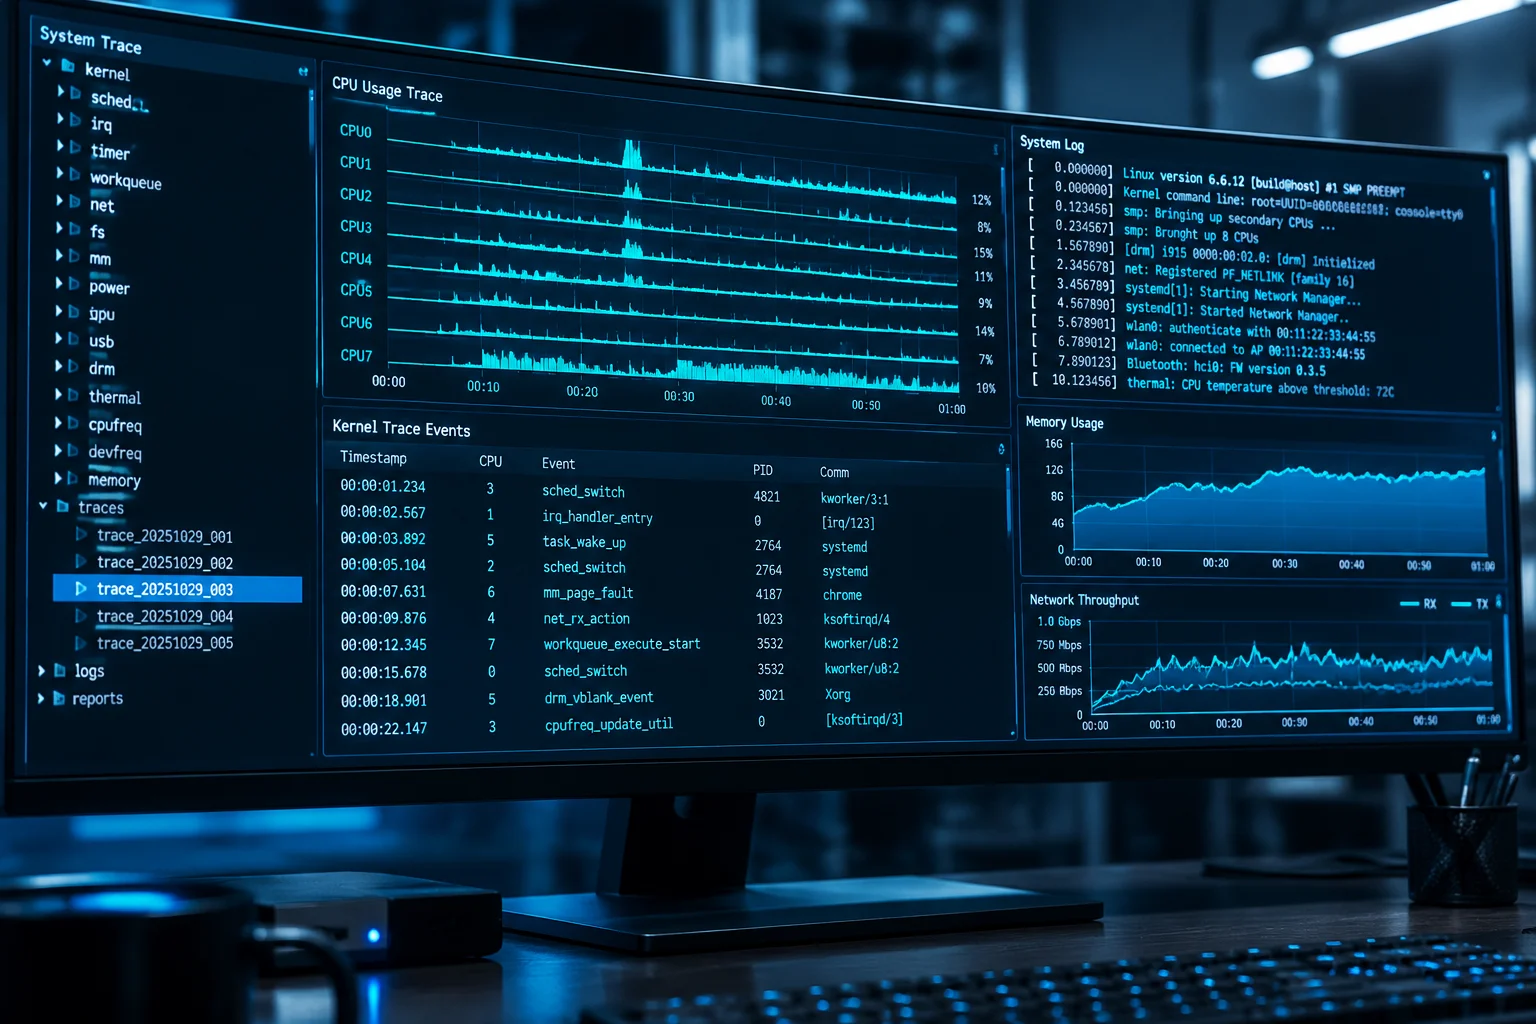
Significant engineering attention targeted memory footprints and peripheral input-output pipelines. Background indexing operations now defer aggressively whenever thermal thresholds or active foreground thread counts elevate, yielding a measurable drop in sustained solid-state drive write operations. Thread scheduling algorithms distribute synthetic routine maintenance tasks across auxiliary hardware cores, leaving primary high-performance execution units unconstrained for interactive workloads.
Modular Service Isolation and Memory Reclamation
System services related to intelligent desktop assistance and context processing now operate inside decoupled worker processes rather than persistent boot-time daemons. If an administrator disables these assistive capabilities via Group Policy, the system unloads associated libraries entirely, reclaiming approximately 420 megabytes of working memory. Traditional inbox utilities continue running without synthetic dependencies, providing a leaner baseline configuration for power users.
Enterprise Reliability and Performance Impact
Fleet deployments and multi-monitor workstations exhibit notable stability enhancements under prolonged stress testing. Virtualization-based security mechanisms have been harmonized with the latest processor hardware extensions, mitigating previously observed frame latency variations in graphics-heavy workflows. Furthermore, base installation media footprints shrank by approximately 2.4 gigabytes through aggressive payload consolidation and retirement of deprecated runtime dependencies.
Upgrade Recommendations and Maintenance
Users planning to initiate deployment should verify storage controller firmware and review local storage capacity before initiating the update. Executing a standard solid-state drive optimization pass and validating system partition health prevents transient installation roadblocks. Organizations maintaining strict endpoint security protocols should test specialized kernel-level inspection software against the revised build prior to extensive domain deployment.